

Reco
Reco secures AI, apps, and agents across the organization. It continuously discovers agents operating inside connected applications — copilots and assistants built into apps like Salesforce, Microsoft 365, and Google Workspace, agents reaching in through MCP servers and OAuth tool grants, and the service accounts and tokens they run as — and shows what each one can reach and what it has done. Reco’s Knowledge Graph turns application, identity, and activity data into context, and its App Factory™ extends that coverage to new apps and AI tools quickly across 200+ integrations.

Catch agent exposure before it becomes an incident
Agents are already operating inside your applications: copilots and assistants shipped into apps you already own, agents reaching in through MCP servers and OAuth tool grants, and the service accounts and tokens they all run as. Most of it arrived without a security review. Reco continuously discovers these agents across connected applications, showing what data each one can reach, what actions it has taken, and where its access came from, so exposure surfaces as it happens instead of at the next audit.
Seemplicity + Reco
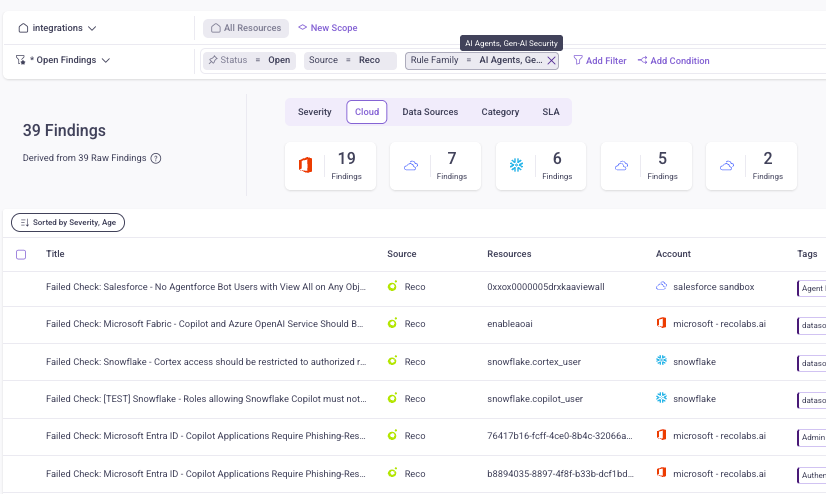
Reco discovers the agents operating across your applications, what they can reach, and how they got that access. Seemplicity ingests those findings and correlates them with other vulnerabilities and exposures already known across cloud, code, and identity. Related findings are grouped where they share a root cause, so thirty people installing the same AI note-taker, or a dozen agents running on the same over-permissioned service account, becomes one fix instead of many separate ones. Each finding arrives with context, gets prioritized alongside everything else Seemplicity tracks, and is routed to whoever owns the affected application or identity, with status tracked through to resolution.
Key Benefits
Most security stacks are good at finding problems and bad at finishing them. An agent finding lands — an assistant reading a tenant’s mail through a grant nobody remembers approving, an agent running on a service account with standing privilege — and from there it’s on someone to notice it, figure out who owns the fix, open a ticket, and follow up until it’s closed. That handoff, more than the finding itself, is where agent risk tends to linger. Bringing Reco’s findings into Seemplicity closes that gap.
- One Queue, Not Another Silo: Agent findings show up in the same workspace as cloud, code, and infrastructure findings, so nothing gets deprioritized just because it lives in a different tool.
- Real Noise Reduction: Instead of thirty separate tickets for thirty people installing the same AI tool, or a dozen tickets for a dozen agents running on one over-permissioned service account, Seemplicity aggregates the same underlying issue into one ticket. Teams fix the root cause once instead of working through duplicate alerts one at a time.
- Faster Ownership: Instead of an agent finding sitting until someone manually figures out who’s responsible, Seemplicity routes it to whoever owns the affected application or identity.
- Less Manual Triage: Security teams don’t have to log into Reco separately to track down what needs attention. Findings flow into the same workflow they’re already using to manage everything else.
- Fast to Turn On: Reco connects via API with no agents to deploy, so teams can start routing Reco findings through Seemplicity without a heavy lift.
Seemplicity Integration Features
Reco continuously discovers agents operating across connected applications, including copilots and assistants built into apps like Salesforce, Microsoft 365, and Google Workspace, agents connecting in through MCP servers and OAuth tool grants, and the service accounts and tokens they run as. The integration brings those findings directly into Seemplicity’s existing workflow.
- Continuous Agent Discovery
Reco scans connected applications on an ongoing basis, surfacing the agents operating inside them, what data they can reach, what actions they’ve taken, and where their access came from, whether that’s a built-in copilot, an MCP connection, or a service account. - Finding Aggregation
Seemplicity groups findings that share the same root cause into a single ticket instead of one per affected agent or grant, so a widely-installed AI tool or an over-permissioned service account becomes one actionable fix rather than a flood of duplicate alerts. - Cross-Source Correlation
Seemplicity correlates Reco’s agent findings with other vulnerabilities and exposures already known across cloud, code, and identity, so agent risk is prioritized alongside everything else instead of sitting in its own silo. - Automated Ownership and Routing
Each Reco finding is routed to whoever owns the affected application or identity, consolidating into one ticket where ownership overlaps and splitting into separate tickets where it doesn’t, without teams needing to log into Reco separately to manage it.