• Why
  • Platform
        • /seemplicity platform
          • Platform OverviewSee how Seemplicity turns findings into fixes
          • IntegrationsBrowse supported tools and integrations
        • Seemplicity Agentic Exposure Action Platform™
          /datasheets & solution briefs
          Seemplicity Agentic Exposure Action Platform™
  • Solutions
        • /by category
          • Exposure Management
          • CTEM – Continuous Threat Exposure Management
          • RBVM – Risk-Based Vulnerability Management
          • Cloud Security
          • Application Security
        • /by need
          • Centralize Exposure Data
          • Reduce Findings Backlog
          • Prioritize High-Impact Risks
          • Automate Vulnerability Remediation Workflows
          • Improve Cross-Team Alignment
          • Ensure Audit-Readiness
        • /by role
          • CISOs
          • Vulnerability Management Leaders
          • Security Engineering / DevSecOps
          • GRC & Compliance
  • Learn
        • /learn
          • Resource CenterYour go-to for learning, exploring, and going deeper
          • Demo CenterSee the product in action through real use cases
          • BlogThe latest on what’s happening in the industry
        • /Mythos Portal

          Your Mythos Learning Center

  • Company
        • /company
          • Our Story
          • Leadership
          • Customers
          • News
          • Careers
          • Partners
          • Contact Us
        • Hertz Case Study
          /customer stories
          Hertz Case Study
  • Search
  • Demo Request

By Need: Reduce Findings Backlog


Datasheets & Solution Briefs
Closing the Find-to-Fix Gap at the Speed of Claude Mythos
How security teams can respond faster in the era of Claude Mythos with Seemplicity’s Agentic Exposure Action Platform.


Datasheets & Solution Briefs
Demystifying Claude Mythos
A security leader’s guide for communicating the shift to agentic defense.

Graphic reading “Application Security Policy: A Practical Guide” beside a stylized policy document with highlighted requirements, checkmarks, and a security lock icon.

May 15, 2026
Application Security Policy: A Practical Guide
Most AppSec policies are written once and ignored. Here’s how to build one that drives fixes.

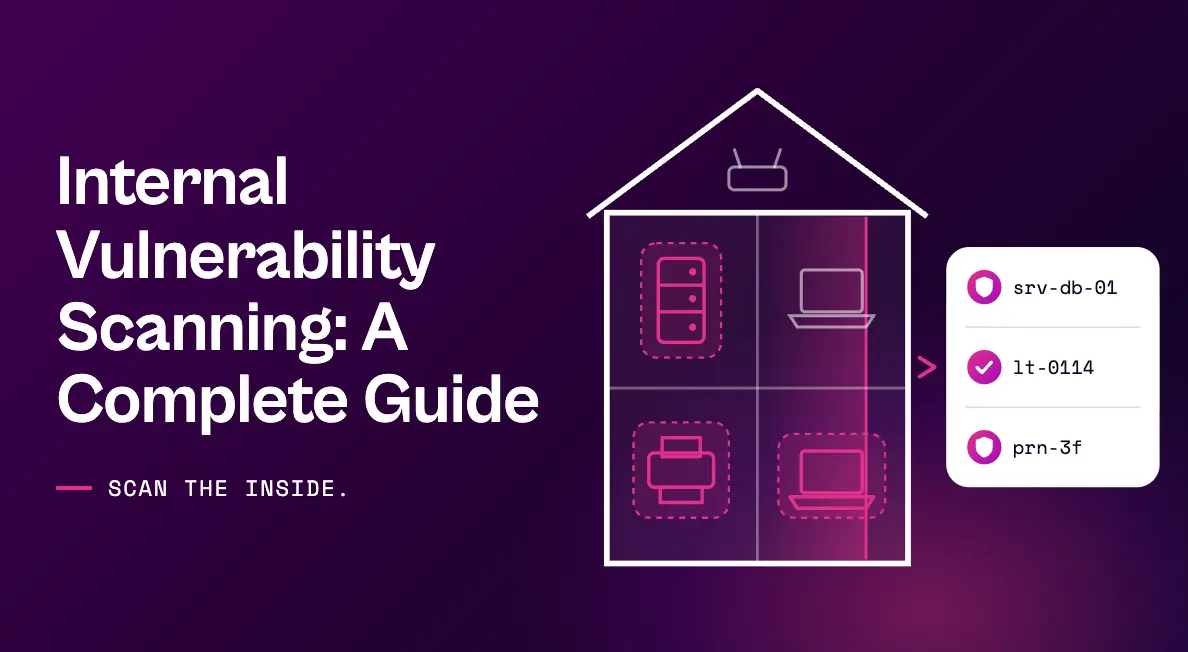
Graphic reading “Internal Vulnerability Scanning: A Complete Guide” beside a network diagram of internal devices being scanned and matched to identified assets.

May 12, 2026
Internal Vulnerability Scanning: A Complete Guide
What internal scans reveal, and how to act on what they find.

Graphic reading “Cloud Security Configuration Management Without the Drift” beside misaligned configuration settings being consolidated into a consistent, standardized set.

May 08, 2026
Cloud Security Configuration Management Without the Drift
Fixing a misconfiguration once is easy. Keeping it fixed is the hard part.


May 06, 2026
Turning Bug Bounty Chaos into Structured Action
Transform unstructured bug bounty findings into actionable fixes by bridging the triage gap with AI-driven remediation workflows.

Attack surface risk management diagram showing discovered assets scored by risk and routed to remediation owners

May 01, 2026
Attack Surface Risk Management Explained
Finding every asset is step one. Reducing the risk they carry is the actual job.


Whitepapers & Research
A New Era in Vulnerability Management
Discover how SANS rates Seemplicity in a hands-on product review covering vulnerability prioritization, automation, and remediation efficiency.

Illustration of four network assets, surrounded by glowing new assets the photo missed, next to the title 'Continuous Attack Surface Management'.

Apr 23, 2026
Continuous Attack Surface Management
Learn all about continuous attack surface management.

  • « Previous
  • 1
  • …
  • 4
  • 5
  • 6
  • 7
  • 8
  • …
  • 13
  • Next »

AI Exposure Response

181 Metro Drive,
San Jose, CA 95110

Yigal Alon St 94, building 2, Floor 14,
Tel Aviv–Yafo, 6789139, Israel

  • Why Seemplicity
  • Platform
    • Overview
    • Integrations
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • Customers
    • News
    • Careers
    • Contact Us
    • Brand
  • Solutions
    • /By Category
      • Exposure Management
      • CTEM – Continuous Threat Exposure Management
      • RBVM – Risk-Based Vulnerability Management
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Why Seemplicity
  • Platform
    • Overview
    • Integrations
  • Solutions
    • /By Category
      • Exposure Management
      • CTEM – Continuous Threat Exposure Management
      • RBVM – Risk-Based Vulnerability Management
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • News
    • Careers
    • Contact Us
    • Brand

Receive future updates 
and announcements.

By subscribing, I consent to receive updates from Seemplicity.

  • Sitemap
  • Terms of use
  • Privacy Policy
  • CSR

All Rights Reserved © 2026 Seemplicity