• Why
  • Platform
        • /seemplicity platform
          • Platform OverviewSee how Seemplicity turns findings into fixes
          • Agentic WorkforceYour dedicated AI security team
          • IntegrationsBrowse supported tools and integrations
        • Seemplicity Agentic Exposure Action Platform™
          /datasheets & solution briefs
          Seemplicity Agentic Exposure Action Platform™
  • Solutions
        • /by category
          • Exposure Management
          • Risk-Based Vulnerability Management (RBVM)
          • Continuous Threat Exposure Management (CTEM)
          • Cloud Security
          • Application Security
        • /by need
          • Centralize Exposure Data
          • Reduce Findings Backlog
          • Prioritize High-Impact Risks
          • Automate Vulnerability Remediation Workflows
          • Improve Cross-Team Alignment
          • Ensure Audit-Readiness
        • /by role
          • CISOs
          • Vulnerability Management Leaders
          • Security Engineering / DevSecOps
          • GRC & Compliance
  • Learn
        • /learn
          • Resource CenterYour go-to for learning, exploring, and going deeper
          • Demo CenterSee the product in action through real use cases
          • BlogThe latest on what’s happening in the industry
        • /Mythos Portal

          Your Mythos Learning Center

  • Company
        • /company
          • Our Story
          • Leadership
          • News
          • Careers
          • Partners
          • Brand
          • Contact Us
        • Hertz Case Study
          /customer stories
          Hertz Case Study
  • Search
  • Demo Request

By Category: Application Security Posture Management (ASPM)

Graphic reading “AI in Application Security: Threat, Defender, and Target” beside a code window connected to icons representing AI as a threat, defensive tool, and attack target.

Aug 05, 2026
AI in Application Security: Threat, Defender, and Target
The three roles AI now plays in AppSec, and how to stay ahead of each.

Illustration of a tower crane lowering a glowing magenta

Aug 04, 2026
How to Implement Application Security Posture Management Tools: A Practical Rollout Plan
The 5-phase plan to roll out application security posture management tools.

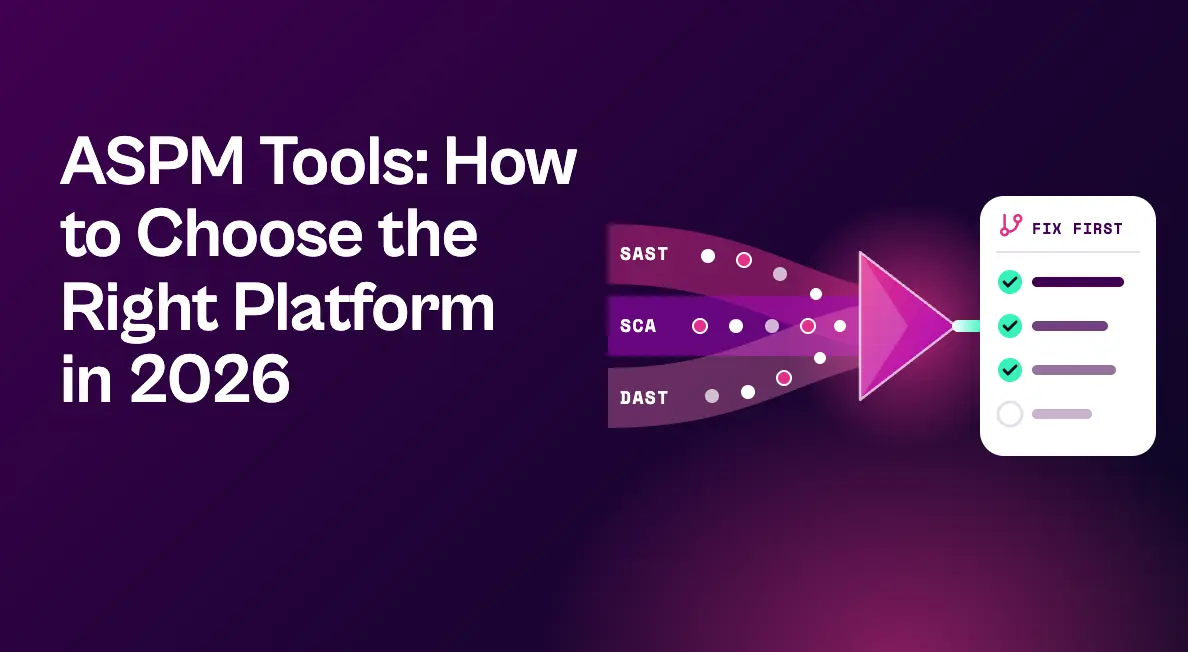
Graphic reading “ASPM Tools: How to Choose the Right Platform in 2026” beside SAST, SCA, and DAST signals converging into a prioritized “Fix First” remediation list.

Jun 19, 2026
ASPM Tools: How to Choose the Right Platform in 2026
The three types of ASPM tools, what to evaluate, and how to choose.


Jun 18, 2026
Application Security Already Knows What’s Broken. Context Is How You Fix It Faster.
Fix application risk at the speed of AI development by shifting from vulnerability visibility to fast, context-driven ASPM action.

A curling receipt lists the hidden costs of an unmanaged AppSec backlog, including triage hours, duplicate tickets, and remediation delays, with a bold magenta “APPROVED” stamp against a dark purple background.

Jun 08, 2026
How to Build the Business Case for ASPM Software
How to pitch ASPM software to leadership and secure buy-in.

Graphic reading “AI AppSec: How to Build an AppSec Program for the AI Era” beside a stylized columned structure representing a strong security foundation, with an upward growth chart and code symbols.

Jun 02, 2026
AI AppSec: How to Build an AppSec Program for the AI Era
Five pillars, a maturity model, and metrics for AppSec in the AI era.

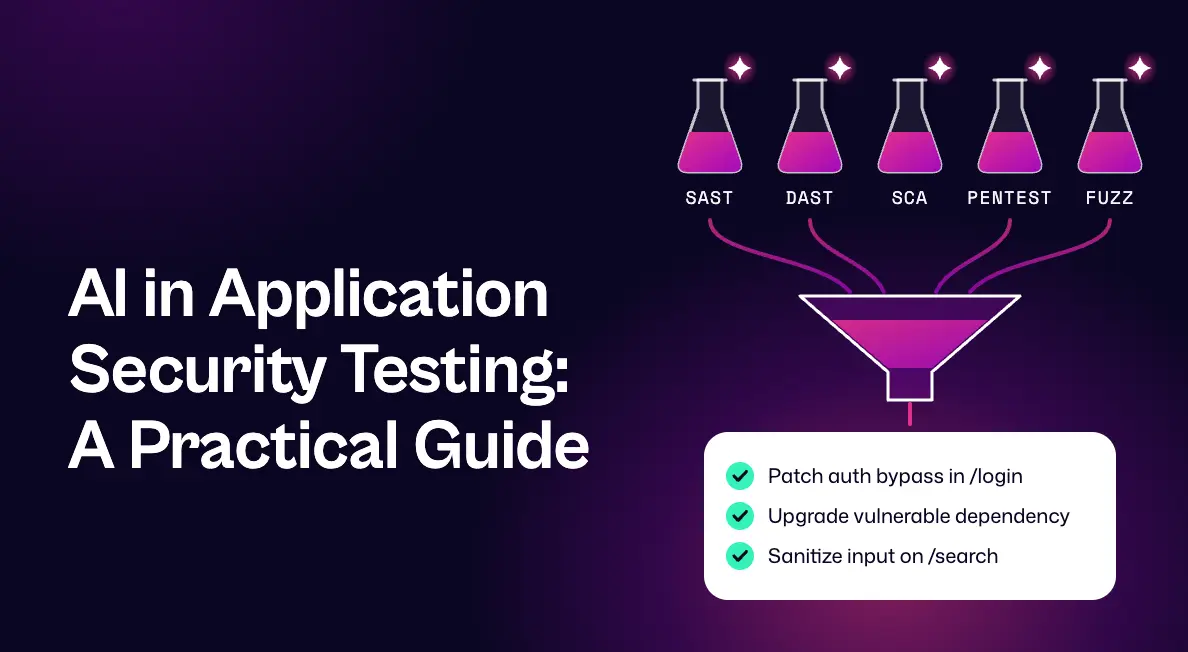
Graphic reading “AI in Application Security Testing: A Practical Guide” beside SAST, DAST, SCA, pentest, and fuzz testing inputs funneling into prioritized remediation actions.

May 29, 2026
AI in Application Security Testing: A Practical Guide
How AI changes each type of AppSec testing, and what it still gets wrong.

Graphic reading “Application Security Policy: A Practical Guide” beside a stylized policy document with highlighted requirements, checkmarks, and a security lock icon.

May 15, 2026
Application Security Policy: A Practical Guide
Most AppSec policies are written once and ignored. Here’s how to build one that drives fixes.

Illustration for improving your application security posture: a vertical stack of glass tiles with app component icons. The misaligned amber and red tiles at the bottom move into a straight, glowing magenta stack at the top, next to a vertical plumb line and a faint upward trend line.

May 03, 2026
How to Improve Your Application Security Posture
Six practical steps to improve your application security posture and measure whether it’s working.

  • 1
  • 2
  • 3
  • Next »

Agentic Exposure Management and Response

181 Metro Drive,
San Jose, CA 95110

Yigal Alon St 94, building 2, Floor 14,
Tel Aviv–Yafo, 6789139, Israel

  • Why Seemplicity
  • Platform
    • Overview
    • AI Agents
    • Integrations
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • News
    • Careers
    • Contact Us
    • Brand
  • Solutions
    • /By Category
      • Exposure Management
      • Risk-Based Vulnerability Management (RBVM)
      • Continuous Threat Exposure Management (CTEM)
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Why Seemplicity
  • Platform
    • Overview
    • Agentic Workforce
    • Integrations
  • Solutions
    • /By Category
      • Exposure Management
      • Risk-Based Vulnerability Management (RBVM)
      • Continuous Threat Exposure Management (CTEM)
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • News
    • Careers
    • Contact Us
    • Brand

Receive future updates 
and announcements.

By subscribing, I consent to receive updates from Seemplicity.

  • Sitemap
  • Terms of use
  • Privacy Policy
  • CSR

All Rights Reserved © 2026 Seemplicity