• Why
  • Platform
        • /seemplicity platform
          • Platform OverviewSee how Seemplicity turns findings into fixes
          • Agentic WorkforceYour dedicated AI security team
          • IntegrationsBrowse supported tools and integrations
        • Seemplicity Agentic Exposure Action Platform™
          /datasheets & solution briefs
          Seemplicity Agentic Exposure Action Platform™
  • Solutions
        • /by category
          • Exposure Management
          • Risk-Based Vulnerability Management (RBVM)
          • Continuous Threat Exposure Management (CTEM)
          • Cloud Security
          • Application Security
        • /by need
          • Centralize Exposure Data
          • Reduce Findings Backlog
          • Prioritize High-Impact Risks
          • Automate Vulnerability Remediation Workflows
          • Improve Cross-Team Alignment
          • Ensure Audit-Readiness
        • /by role
          • CISOs
          • Vulnerability Management Leaders
          • Security Engineering / DevSecOps
          • GRC & Compliance
  • Learn
        • /learn
          • Resource CenterYour go-to for learning, exploring, and going deeper
          • Demo CenterSee the product in action through real use cases
          • BlogThe latest on what’s happening in the industry
        • /Mythos Portal

          Your Mythos Learning Center

  • Company
        • /company
          • Our Story
          • Leadership
          • News
          • Careers
          • Partners
          • Brand
          • Contact Us
        • Hertz Case Study
          /customer stories
          Hertz Case Study
  • Search
  • Demo Request

By Role: Security Engineering / DevSecOps

AppSec automation workflow diagram showing scanner findings flowing through dedupe and routing into developer tickets and fixes.

May 14, 2026
Why AppSec Automation Stalls After Detection
Your scanners are automated. Your remediation probably isn’t. Here’s how to close that gap.


May 13, 2026
Why I Joined Seemplicity: A Note From Our New VP of Sales
Seemplicity’s new VP of Sales shares why the future of cybersecurity depends on scalable remediation execution.

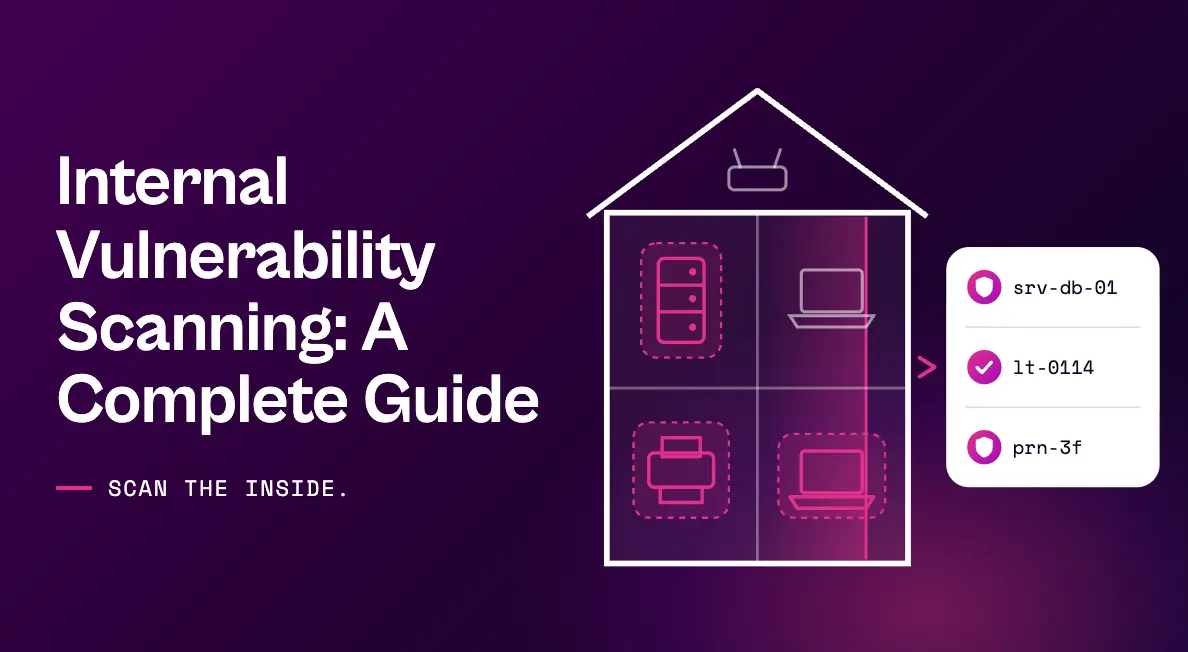
Graphic reading “Internal Vulnerability Scanning: A Complete Guide” beside a network diagram of internal devices being scanned and matched to identified assets.

May 12, 2026
Internal Vulnerability Scanning: A Complete Guide
What internal scans reveal, and how to act on what they find.


Webinars
Scaling Exposure Management for Mythos Velocity
Moving from manual patch cycles to machine-speed remediation.


May 06, 2026
Turning Bug Bounty Chaos into Structured Action
Transform unstructured bug bounty findings into actionable fixes by bridging the triage gap with AI-driven remediation workflows.

Illustration for improving your application security posture: a vertical stack of glass tiles with app component icons. The misaligned amber and red tiles at the bottom move into a straight, glowing magenta stack at the top, next to a vertical plumb line and a faint upward trend line.

May 03, 2026
How to Improve Your Application Security Posture
Six practical steps to improve your application security posture and measure whether it’s working.

Attack surface risk management diagram showing discovered assets scored by risk and routed to remediation owners

May 01, 2026
Attack Surface Risk Management Explained
Finding every asset is step one. Reducing the risk they carry is the actual job.

Blog thumbnail reading

May 01, 2026
Do You Need an ASPM Platform? 6 Signs It’s Time
6 signs it’s time you need an ASPM platform.


Whitepapers & Research
A New Era in Vulnerability Management
Discover how SANS rates Seemplicity in a hands-on product review covering vulnerability prioritization, automation, and remediation efficiency.

  • « Previous
  • 1
  • …
  • 4
  • 5
  • 6
  • 7
  • 8
  • …
  • 15
  • Next »

Agentic Exposure Management and Response

181 Metro Drive,
San Jose, CA 95110

Yigal Alon St 94, building 2, Floor 14,
Tel Aviv–Yafo, 6789139, Israel

  • Why Seemplicity
  • Platform
    • Overview
    • AI Agents
    • Integrations
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • News
    • Careers
    • Contact Us
    • Brand
  • Solutions
    • /By Category
      • Exposure Management
      • Risk-Based Vulnerability Management (RBVM)
      • Continuous Threat Exposure Management (CTEM)
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Why Seemplicity
  • Platform
    • Overview
    • Agentic Workforce
    • Integrations
  • Solutions
    • /By Category
      • Exposure Management
      • Risk-Based Vulnerability Management (RBVM)
      • Continuous Threat Exposure Management (CTEM)
      • Cloud Security
      • Application Security
    • /By need
      • Centralize Exposure Data
      • Reduce Findings Backlog
      • Prioritize High-Impact Risks
      • Automate Vulnerability Management Workflows
      • Improve Cross-Team Alignment
      • Ensure Audit-Readiness
    • /By role
      • CISOs
      • Vulnerability Management Leaders
      • Security Engineering / DevSecOps
      • GRC & Compliance
  • Learn
    • Resource Center
    • Demo Center
    • Blog
    • FAQs
  • Company
    • Our Story
    • Leadership
    • News
    • Careers
    • Contact Us
    • Brand

Receive future updates 
and announcements.

By subscribing, I consent to receive updates from Seemplicity.

  • Sitemap
  • Terms of use
  • Privacy Policy
  • CSR

All Rights Reserved © 2026 Seemplicity